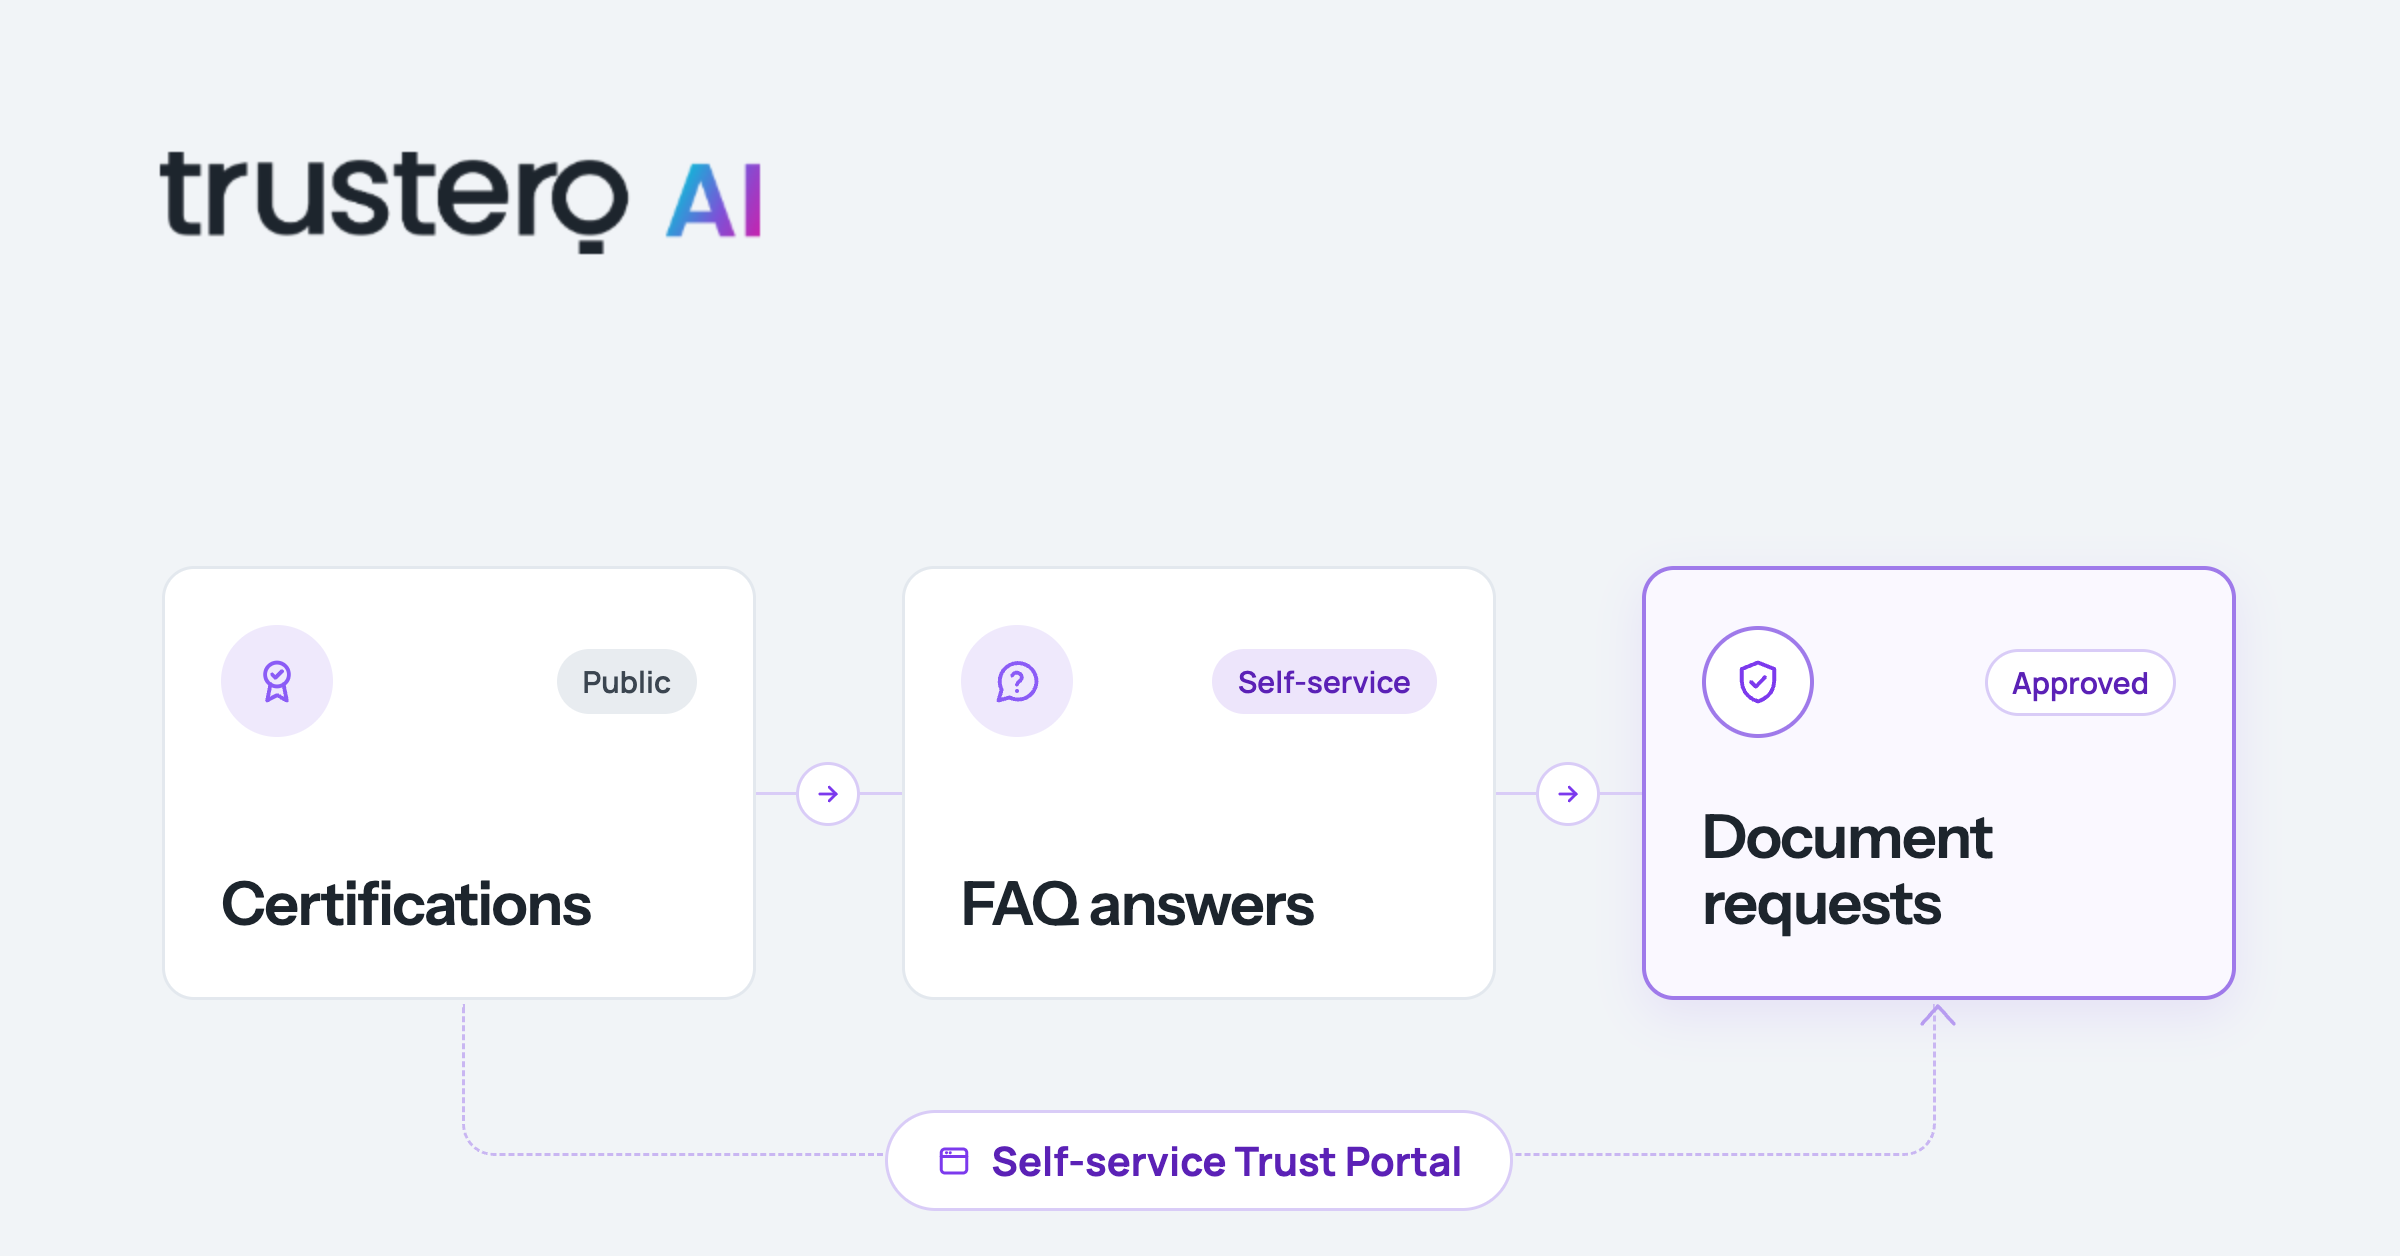

Requests for reports, certifications, and attestations keep arriving. Alongside them are questions your FAQ already answers. Each request may be straightforward, but together they create an email bottleneck that pulls GRC and security teams into repetitive work.
The information is often already prepared. The remaining work is locating it, checking whether it can be shared, responding, and tracking the request. When every reviewer has to email someone to get started, the team ends up hand-delivering its own assurance information.
A self-service trust portal can reduce that handling time by giving reviewers a place to find approved answers and documents, and to request material that needs approval. The goal is to save team time without giving up control: routine information becomes easier to access, while individual document requests remain reviewable and trackable.
Stop treating every document request as new work
A request for an existing report does not necessarily require new analysis. But handling it through email can still involve finding the right document, confirming its sharing conditions, responding to the requester, and following up.
Repeat that process for certifications, attestations, and other assurance materials, and document delivery becomes routine. The information may be reusable, but the team’s effort is not.
A trust portal gives that information a consistent destination. Material approved for public access can be available without a separate email request. Documents that need closer oversight can follow a request-and-approval process instead. Reviewers have a place to start, and the team doesn't have to personally deliver every item.
For GRC teams, audit firms, and managed security service providers, the design question is the same: which requests need someone’s expertise, and which simply need a reliable route to existing information?
People will keep asking for assurance. The aim is to keep each request from turning into another round of manual coordination.
Put FAQ answers where reviewers are looking
Publishing an FAQ is only part of the job. If reviewers encounter it only after emailing a question, the answer exists, but the team is still doing the work of delivering it.
Putting FAQs alongside assurance documents gives reviewers a chance to find both the information and the context they need. Instead of switching between an email exchange and a separate document search, they can start in one place.
Illustrative FAQ questions might include where to find available certifications, how to request a report, or where to see updates. For standard, approved answers, those questions should have a self-service path rather than require a specialist to compose another response.
A practical starting point is the team’s existing inbox. Identify questions that recur, check whether the FAQ already answers them, and make those answers easier to find. If a question keeps returning, the answer may need clearer wording or a more obvious location.
Here, self-service saves time without removing a necessary decision. The answer is already prepared; the reviewer just needs a better way to reach it.
Approve and track document requests without relying on email chains
Not every document belongs in a public library. A request for a sensitive attestation may require review, even when other assurance information is openly available. Self-service should make that review easier to manage while keeping it in place.
Trustero’s Trust Portal allows teams to approve and track individual document requests. That provides a way to handle requests for reports, certifications, and attestations without making an email thread the primary way to coordinate each one.
Consider an illustrative review. A visitor reads an FAQ, accesses a certification the organization has chosen to make public, and requests an attestation that requires approval. The team reviews that specific document request rather than manually handling every step of the visitor’s information gathering.
The request still deserves a decision. The difference is that routine discovery and access to public information do not need to wait for the same person who handles sensitive disclosures.
Request tracking is a separate job from making documents available. Providing a document and tracking the request are related but distinct parts of the work.
This distinction should shape expectations: a portal may still receive plenty of legitimate document requests. The intended improvement is fewer repetitive emails and manual handoffs around those requests, with necessary approvals still in place.
Keep self-service within clear sharing boundaries
The time-saving case for self-service depends on knowing what people can access independently and what needs review. Without those boundaries, a team may either expose too much or add unnecessary friction to information it is comfortable sharing.
Trustero’s Trust Portal provides Public, Confidential, and Restricted document settings. A click-through NDA can be required based on the restriction or permission configured for a document. These settings should reflect deliberate choices about the document’s audience and sharing conditions.
An NDA and an access approval serve different purposes. One addresses confidentiality terms; the other addresses whether the requester should receive the information. Teams should define both rather than treating either as a substitute for the other.
Publication decisions also deserve their own oversight. A document can be approved for inclusion in the portal without being approved for unrestricted public access.
Publisher and approver roles, along with a preview option before publishing, support that distinction. Teams can define who prepares the information, who approves publication, and what must be checked before it goes live. That review should cover the content and its document permissions as well as how the page looks.
Measure the repetitive work your team no longer has to do
A portal should save the team more work than it takes to maintain. Start by checking whether reviewers can get what they need without someone intervening at each stage.
Evaluate the recurring report requests that still arrive by email, the questions already covered by the FAQ, and the exchanges needed to complete a document request. Those observations can help identify where self-service is working and where the experience still sends people back to the inbox.
Request and activity tracking provide visibility, but activity alone doesn't prove time saved. The outcome to look for is less repeated document delivery and fewer routine replies, leaving the team more capacity for access decisions and questions that require expertise.
Keeping the portal current also requires ownership. FAQs need to reflect the questions people are asking, and shared information needs attention when it changes. An update log and subscription option can support ongoing communication rather than making every update another individual email exchange.
This is the practical role of Trustero’s Trust Portal: combine self-service assurance information with controlled, trackable document requests. Customizable branding and a company-domain URL make the destination recognizable, and its main job is helping reviewers and the team complete their work.
Give routine requests a self-service path. Save the team’s time for the questions and decisions that need its judgment.
Explore Trustero’s Trust Portal: https://www.trustero.com/products/trust-portal